

5 min read
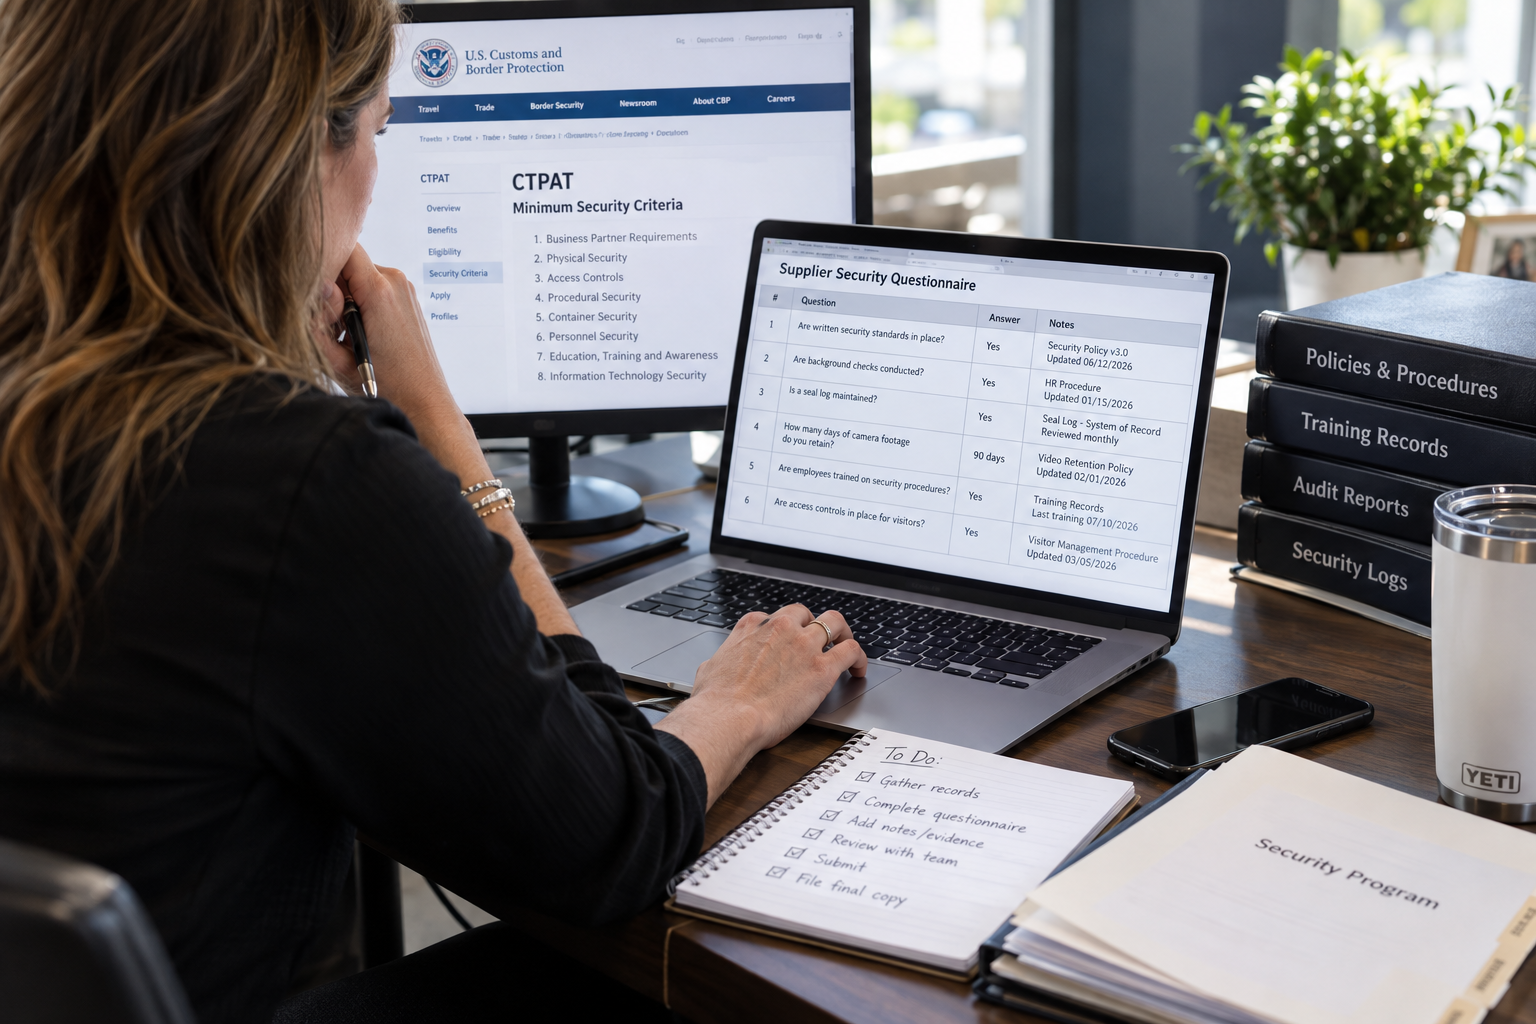
Answer a CTPAT security questionnaire from your records, not from memory. These forms run 50 to 60 yes/no questions mapped to the Minimum Security Criteria, and every yes is a claim you have to be able to produce dated evidence for later, either to that customer or to CBP. Pull each answer from your system of record, use the notes field to name the artifact and its date, and give an honest no with a remediation date rather than a yes you can't back.
A customer just sent you a 53-question form
It arrives from procurement or from the customer's global security team. Two-week turnaround. It gets forwarded to whoever owns compliance, and it looks like paperwork.
It isn't. It's a written record of what you claim your security program does, held by a company that can audit you.
Most teams treat these as an administrative task and answer them the way you'd answer any vendor form. Quickly, from memory, optimistically. That approach works right up until the day someone asks to see the thing you said you had.
What a customer CTPAT security questionnaire actually asks
Two real examples, both publicly posted by the companies that send them.
The Gebrüder Weiss importer security questionnaire runs more than 60 questions across eight sections: business partner requirements, physical security and access controls, procedural security and documentation processing, container security, personnel security, education and training awareness, information technology security, and a catch-all for other measures. Answers are Yes, No, or N/A, with a notes field.
Eli Lilly's runs 53 questions across eight sections of its own, weighted differently: nine questions on seal security alone, 17 on people and physical security, 10 on physical access controls and visitors.
Both map to the CTPAT Minimum Security Criteria. That's not a coincidence. Your customer is a CTPAT member with an obligation to vet its business partners, and the fastest way to do that is to hand you the criteria as a checklist.
Some questions ask for real specificity. Lilly's seal question asks whether you keep a log documenting seal number, container number, date, customer name, carrier name, and the name of the warehouse employee who applied the seal. Another asks how many days of camera footage you retain. Others ask for inspection checklists with dates, times, and inspector names.
But most of it is binary. Are written standards in place. Are background checks conducted. Are passwords changed periodically. Yes or no.
That's the whole problem.
Why yes/no is the trap
A binary form is fast to complete and hard to survive.
Nothing stops you from checking yes on all 53. The form doesn't ask for attachments. Nobody's going to read a procedure over your shoulder. So the path of least resistance is a column of yeses and a signature.
Then two things happen to that record.
Your customer files it. If the relationship grows, or if something goes wrong in a lane, they escalate to an onsite audit. The auditor walks in holding your answers and asks to see what you said you had.
And CBP asks the same questions. The questionnaire was built from the MSC, so your next revalidation covers the same ground with a different auditor, and now there's a written answer sitting with a customer that has to match what you tell CBP.
This is where programs get caught, and it's almost never dishonesty. It's answering from memory. Someone remembers that a procedure was written, checks yes, and nobody opens the document to find that it was last revised in 2021 and names a shift supervisor who left two years ago.
The yes was true once. That's not the same as true now.
How to answer a CTPAT security questionnaire
Start from your evidence, not from the form. Before you answer anything, pull the current state of each MSC area: what exists, who owns it, when it was last updated. Then answer against that. Working in the other direction, reading a question and reaching for what you remember, is how a program ends up with answers it can't support.
Answer at the level of evidence you actually hold. A written procedure with no training records behind it is a different answer than a procedure your team has been trained on and tested against. If the question asks whether employees are trained on a policy and you have the policy but not the records, that's a partial, and there's a way to say so.
Use the notes field. Every one of these forms has one and most people leave it blank. Name the artifact and its date. "Yes. Seal log maintained in our system of record, reviewed monthly, last review August 2026." One sentence turns an assertion into something checkable, and it tells a reviewer you're working from records rather than recall. It also saves you later, because you'll know exactly what you meant.
Use N/A only when it's true, and say why. N/A is the most abused box on these forms. If you don't handle containers, N/A on container security is correct and you should write the reason. If you're using it to avoid a question that does apply to you, a reviewer will notice, and it reads worse than a no.
Keep the completed questionnaire. Date it, record who answered it, and file it where you can find it. Your next one from the same customer will be compared against this one, and so will anything you tell CBP.
Three answers that cause problems later
Yes on a written procedure nobody has opened. Check the revision date before you answer. If it's stale, you have a fast fix: update it, then answer yes with the new date in the notes.
Yes on logs that have gaps. Seal logs, visitor logs, and inspection checklists are the first things an onsite auditor pulls, because they're dated and easy to spot-check. A log with three missing weeks turns a yes into a finding.
N/A used as a dodge. Covered above, and worth repeating, because it's the single most common thing that gets flagged when a questionnaire turns into an audit.
When the honest answer is no
This is the part nobody prepares for, and it's where most of the value is.
A dated no with a plan is a stronger answer than a yes you can't support.
Your customer isn't running a pass/fail exam. They're running a risk assessment, and what they're really measuring is whether you know your own program. "No. Written procedure in development, target Q4 2026, owned by our facility security manager" tells them you've looked, you know where the gap is, and someone owns closing it. That's a program with visibility.
A yes that collapses six months later during an onsite audit tells them the opposite, and it costs you the relationship you were protecting when you wrote it.
The obligation that comes with the honest no is simple. Hit the date.
The same evidence answers CBP and your customer
Every question on that form maps back to an MSC requirement, which means the evidence base that satisfies your customer is the same one CBP asks for at revalidation. Build it once and both audiences pull from it. If assembling it for this questionnaire took three weeks of digging, that's worth knowing now, because what CBP looks at during revalidation has moved in the same direction, and where your evidence actually lives is usually the reason it took that long.
Worth remembering that you're on both sides of this. The same criteria you're answering against are the ones you're expected to send to your own business partners.
Frequently asked questions
Can I send our CTPAT certificate instead of completing the questionnaire?
Usually not. Certification tells your customer you met the criteria at your last validation. The questionnaire asks about the specific facility, lane, or relationship they're buying from. Send the certificate along with the completed form, not in place of it.
Do we have to answer if we're not CTPAT certified?
If you want the business, yes. CTPAT members are required to vet their business partners, and a non-member partner gets vetted through exactly this kind of questionnaire. Not being certified isn't a reason to skip it. It's the reason you received it.
How long should it take?
If your evidence is current and lives in one place, a 53-question form is a few hours. If it takes three weeks of chasing people, the questionnaire isn't your problem. It's the diagnostic.
What if the questionnaire asks for something the MSC doesn't require?
It happens. Customers layer their own requirements on top of the criteria, especially on camera retention and background checks. Answer it honestly, note in the field that it sits outside CTPAT's requirements, and treat it as a commercial term to discuss rather than a compliance failure.